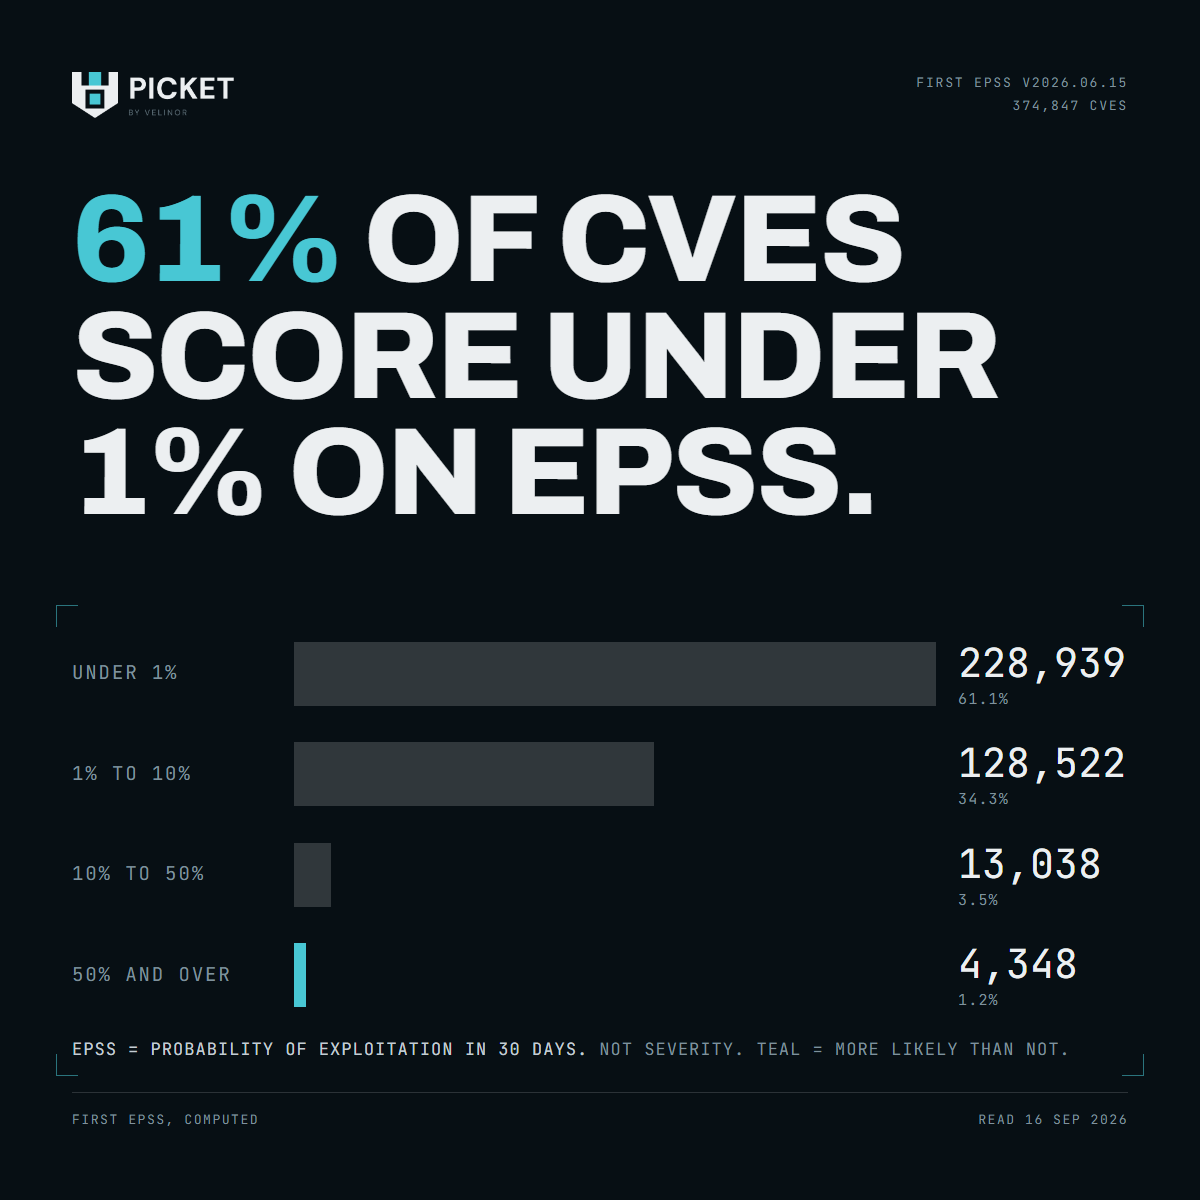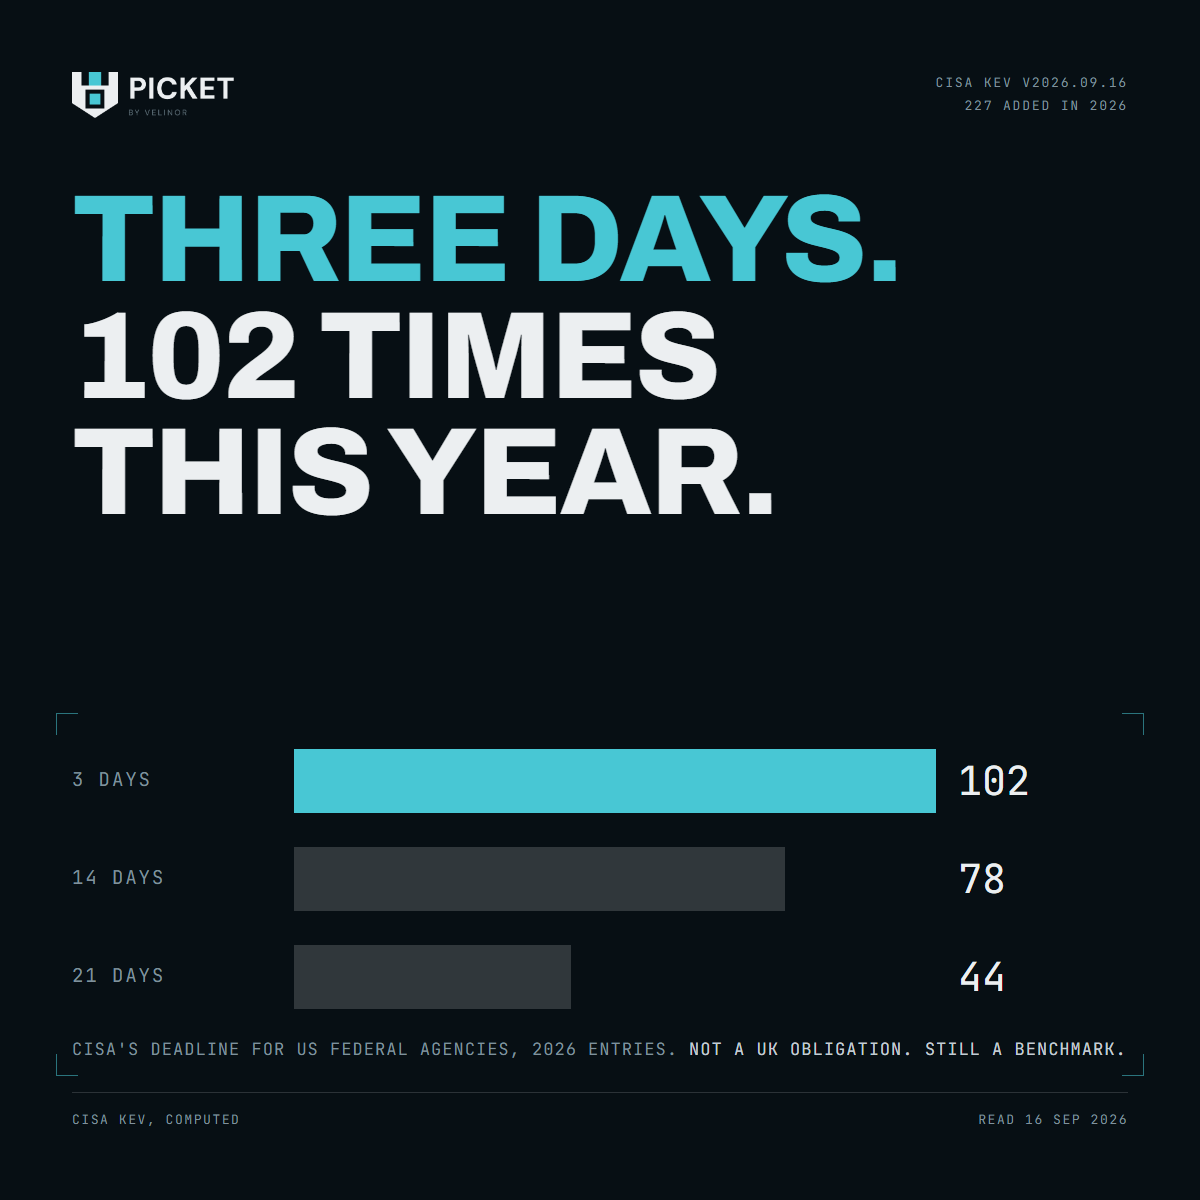
Every input to vulnerability prioritisation is public except one. CVSS is published. EPSS is published. The KEV list is published. The only thing nobody else can give you is how much each system matters to your business.
That is the criticality matrix. From my time running vulnerability management within the MOD, it is the step most programmes skip, because it feels like admin. It is the step that makes the rest of the ranking yours.
How to build one in ninety minutes.
- List the systems, not the hosts. Twenty to forty lines covers most organisations.
- For each, answer three questions in the words of the person who runs that part of the business. What stops if it goes down. What leaks if it is read. Who is on the phone within the hour.
- Give each a tier. Three tiers are enough. More than four and nobody maintains it.
- Write down who agreed it and when.
Then feed the tier into your ranking, so that a medium on a tier one system can outrank a high on a tier three system.
Without that step your ranked list is the same as everyone else's, and everyone else's list is the internet's opinion of your estate.