Control 2402 of Def Stan 05-138 Issue 4 is the one an assessor will use to test your vulnerability management. It applies at Cyber Risk Profile Levels 1, 2 and 3. Verbatim, it asks for three things.
- Vulnerability scans on a monthly basis and during any major system or application updates.
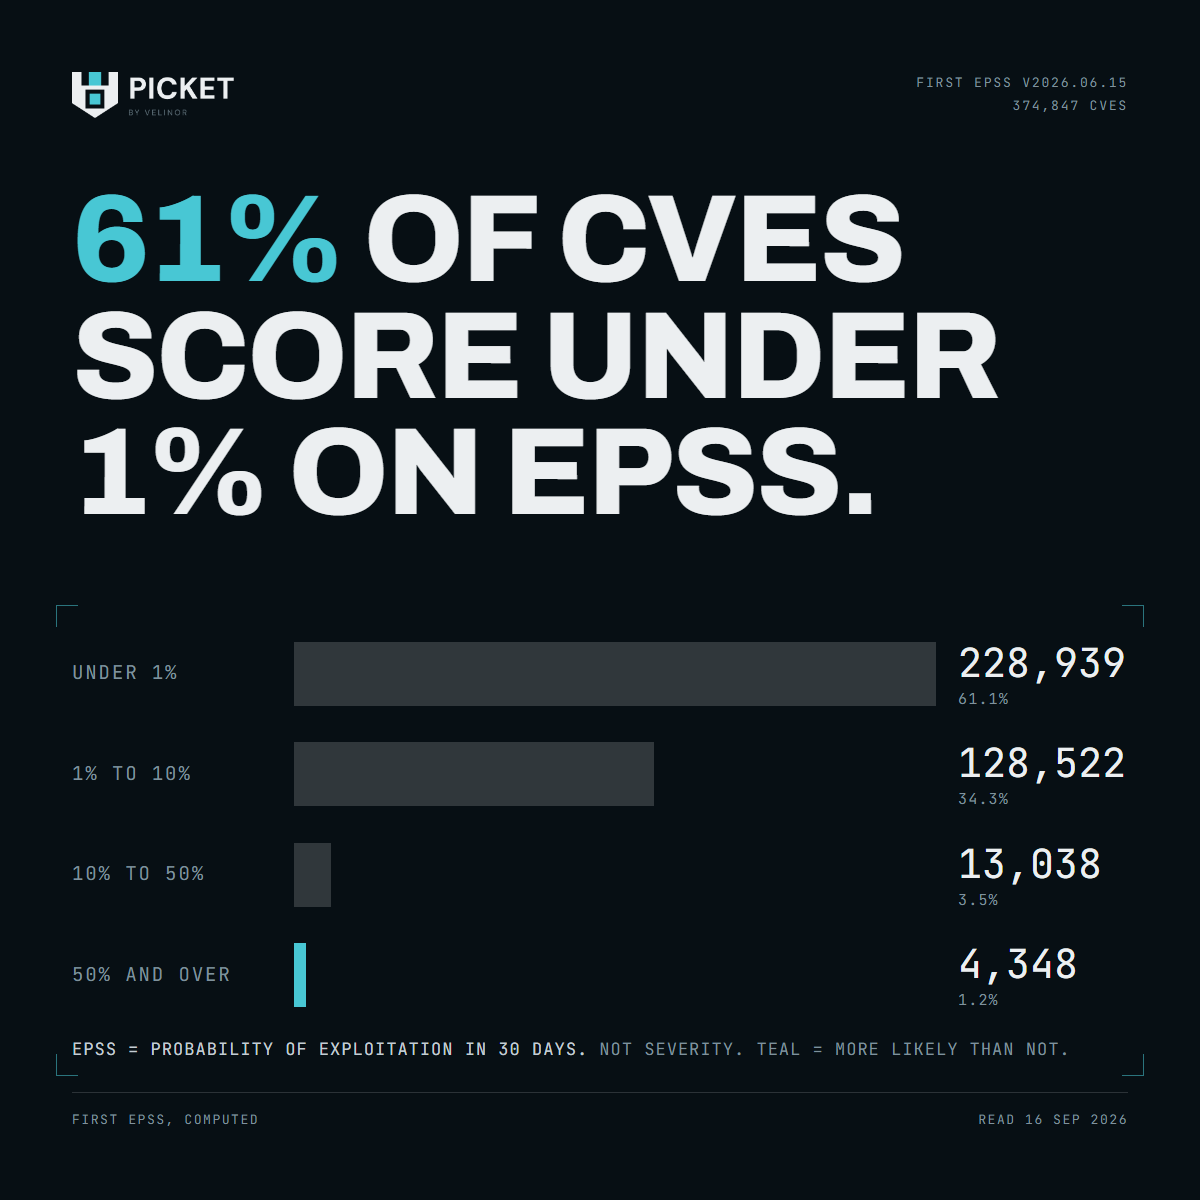
- Vendor patches or fixes prioritised using CVSS v3 scoring.
- A Risk Treatment Plan to address identified vulnerabilities.
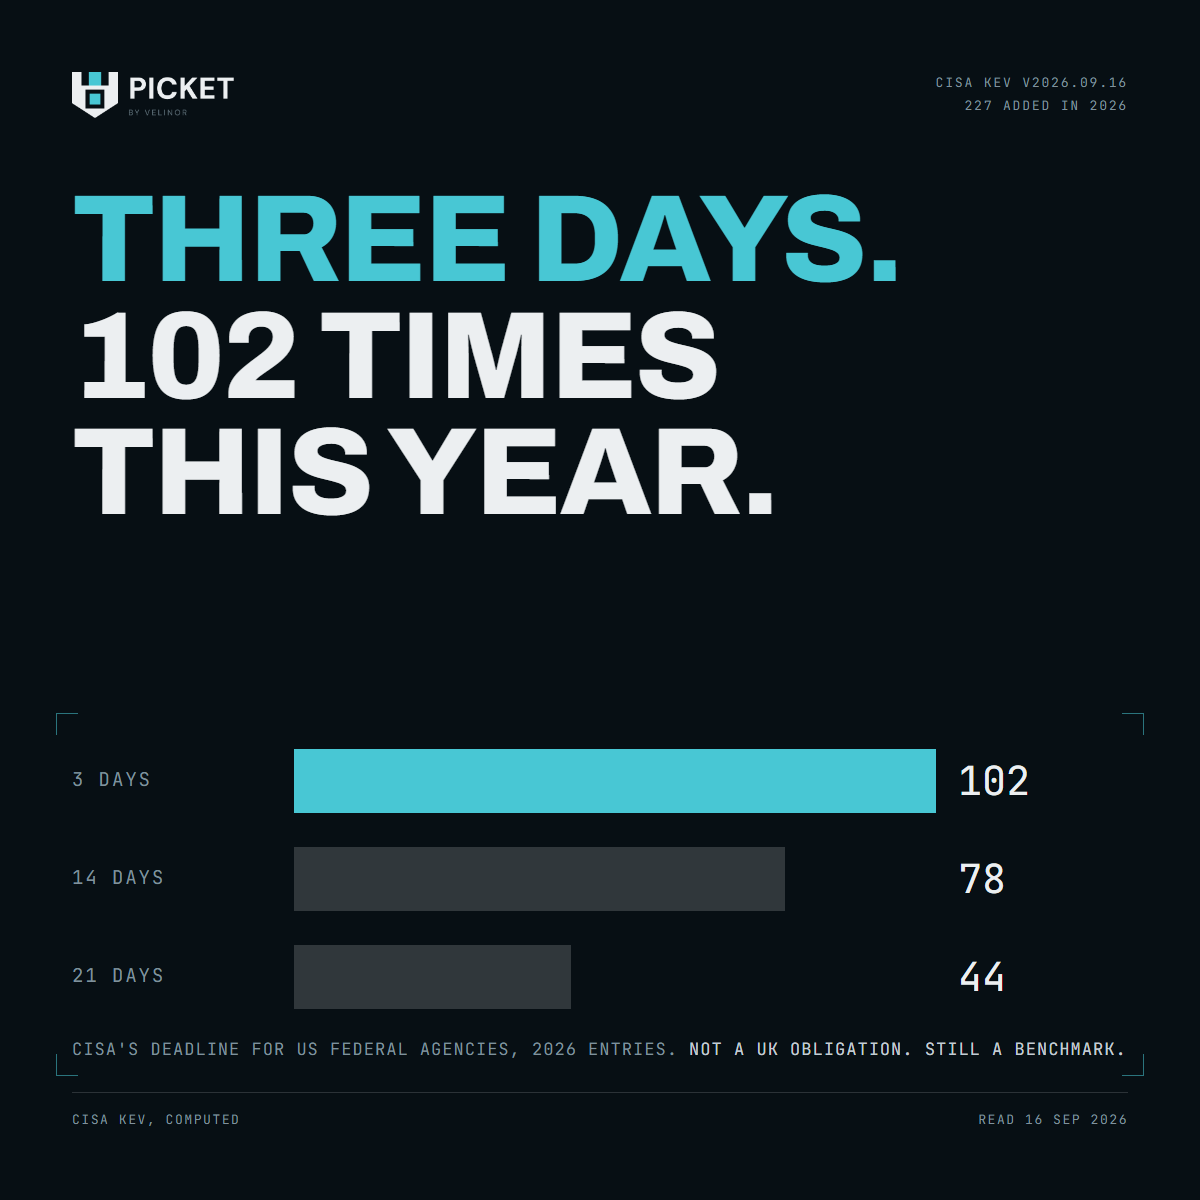
Then: vulnerabilities addressed in accordance with the Supplier's internal remediation timelines and in line with reasonable industry standards.
Two things people get wrong about it.
First, the scan cadence is fixed. Monthly. A quarterly scan does not meet it, however good the report.
Second, the remediation timeline is not fixed. The standard points at your own policy and asks whether you met it. That means the policy you write is the thing you will be assessed against. Write one you can meet, then keep the evidence that you did.
What an assessor will ask for: dated scan reports for each month, the treatment plan, and the record of what was fixed, accepted or deferred, and why.