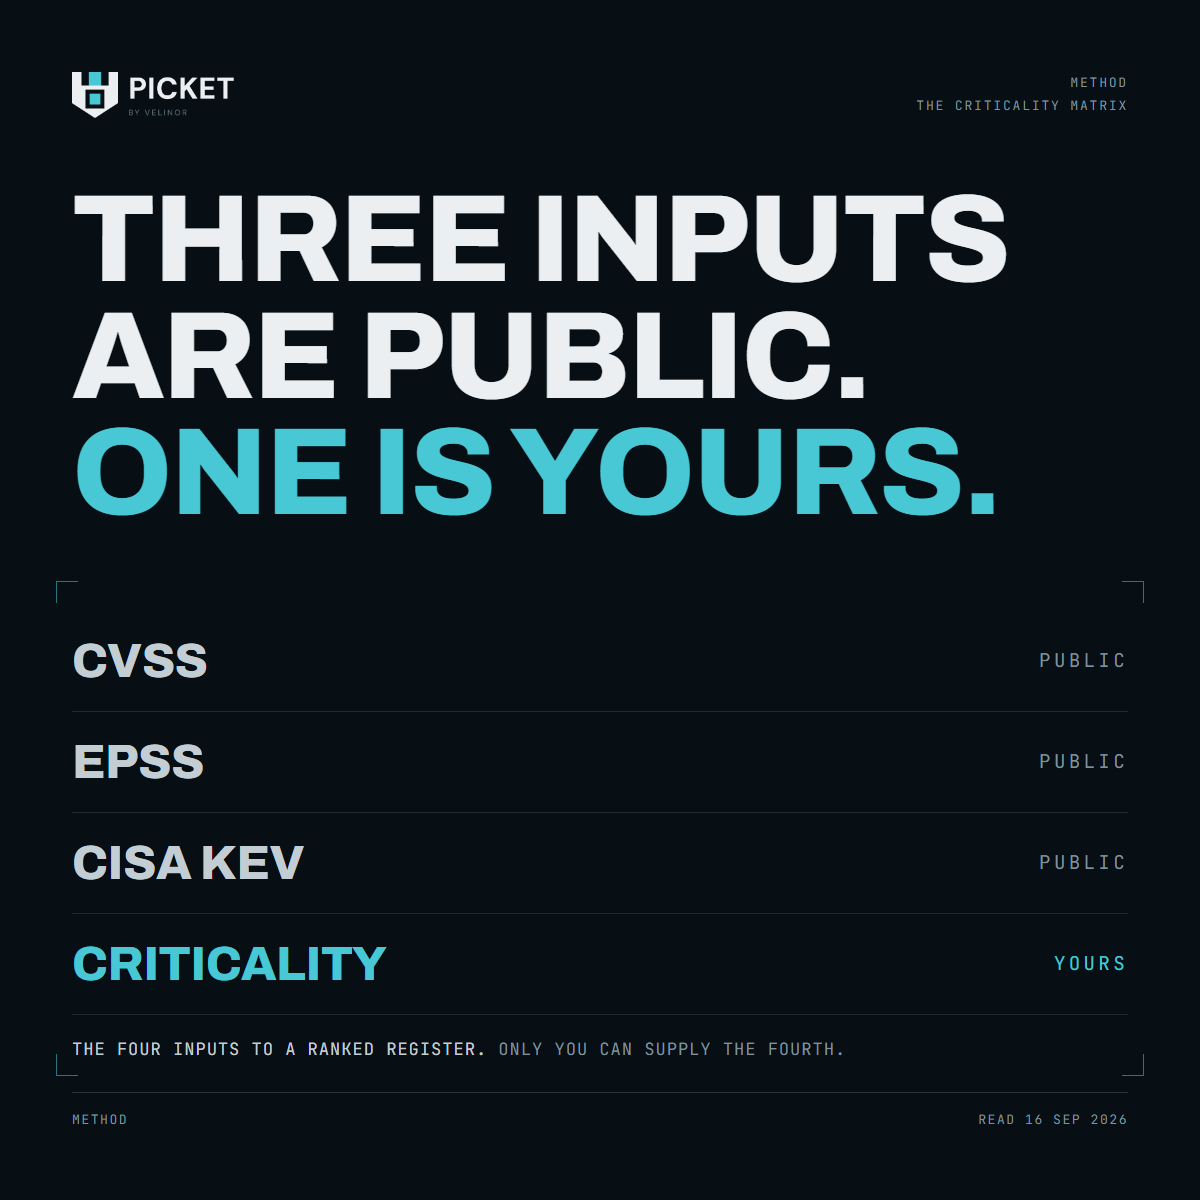
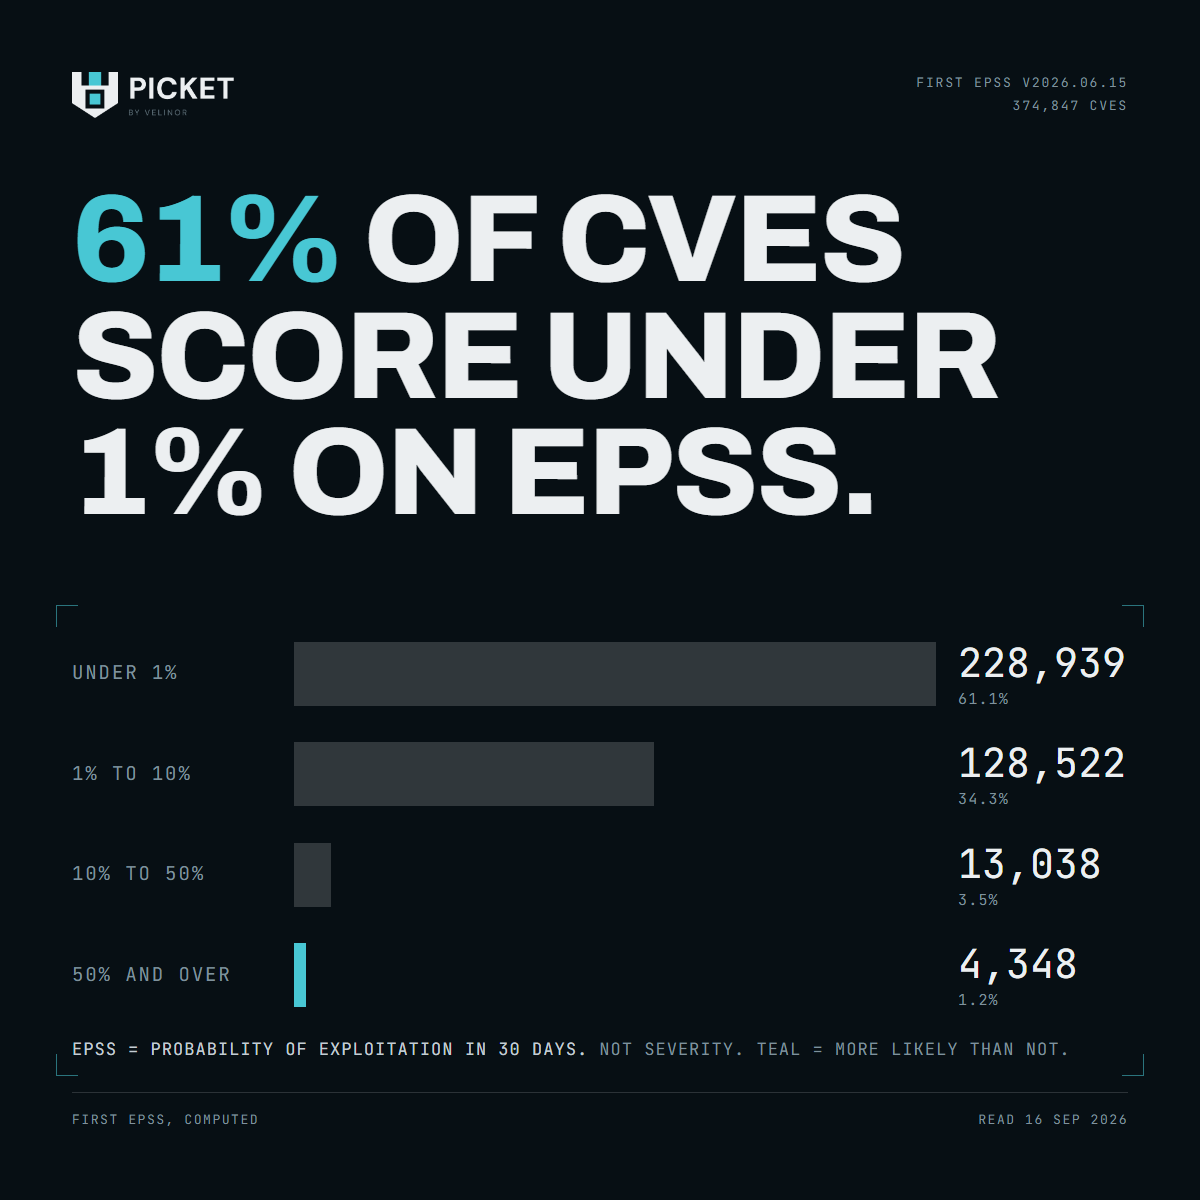
EPSS is the number most vulnerability tools now show next to CVSS, and it is widely read wrong.
What it is. The Exploit Prediction Scoring System, run by FIRST, gives every CVE a probability that it will be exploited in the wild in the next 30 days. It is updated daily from observed exploitation activity.
What it is not.
- It is not severity. A CVE can be rated critical and carry an EPSS under 1%. Many do.
- It is not a statement about your estate. It is a statement about the CVE across the whole internet.
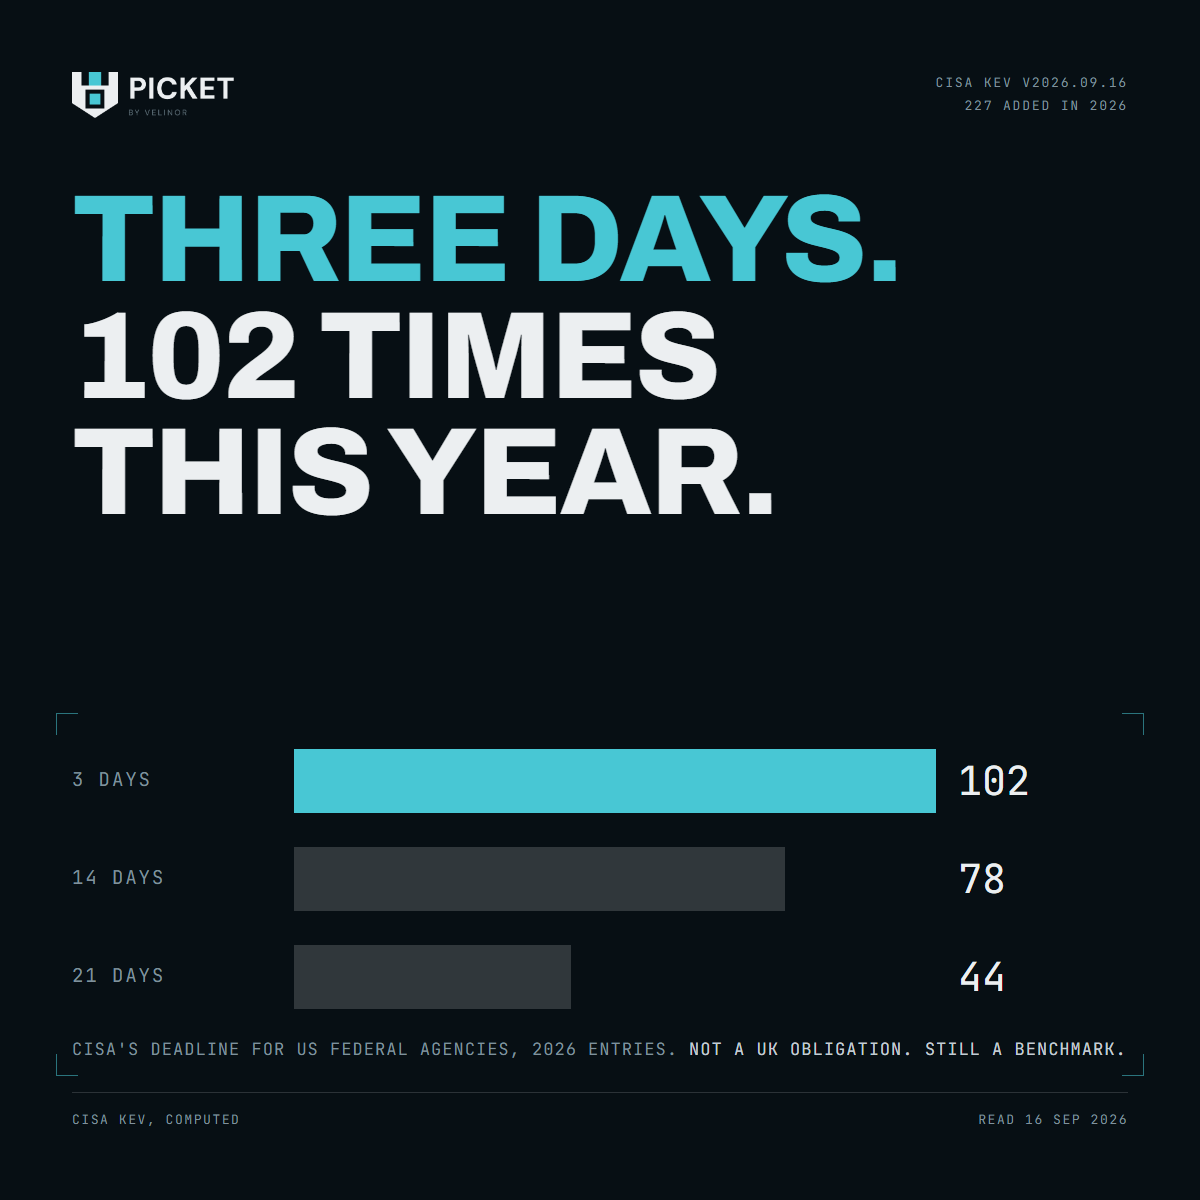
- It is not proof. A high EPSS means attackers are likely to try. A KEV entry means they already have.
How to use it. Sort by EPSS within severity, not instead of it. Then put anything on the KEV list at the top regardless of either. Then ask which of the remaining findings sit on systems that matter to your business.
That order takes a list of thousands down to a list you can fix this month.