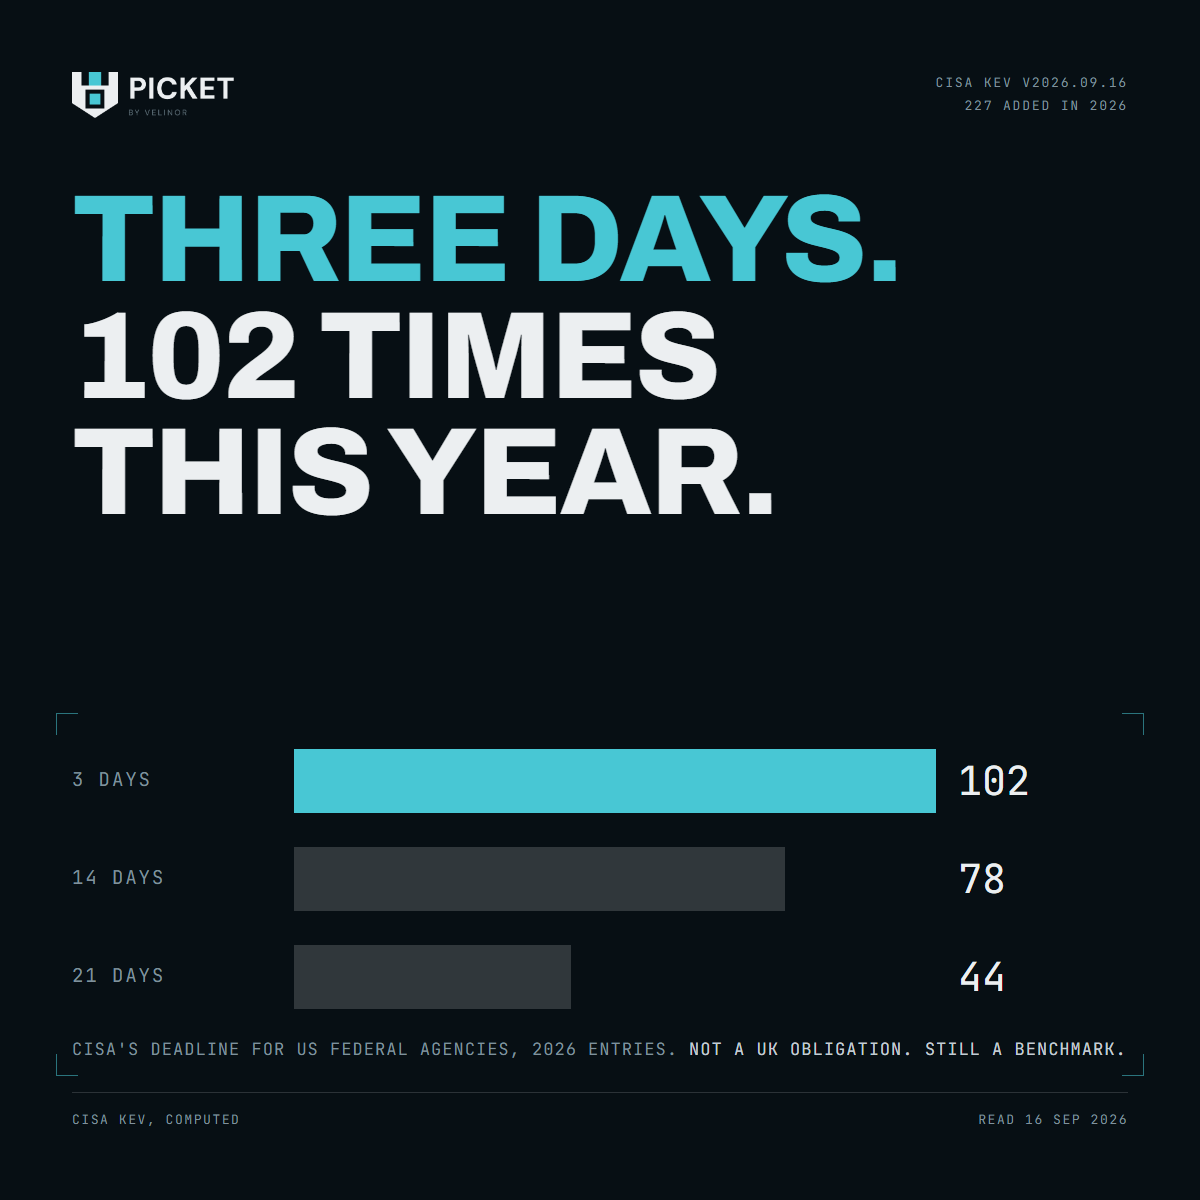
When CISA adds a vulnerability to its Known Exploited list it sets a date by which US federal agencies must act. Of the 227 entries added in 2026:
- 102 got three days.
- 78 got fourteen days.
- 44 got twenty-one days.
That clock binds US federal agencies and FedRAMP cloud providers. It does not bind a UK company. But it is the most experienced vulnerability programme in the world telling you how long it thinks you have, in a public file, for free.
If your own remediation policy gives every critical finding thirty days, it is slower than CISA on four out of five of this year's exploited entries. An assessor comparing the two will notice.