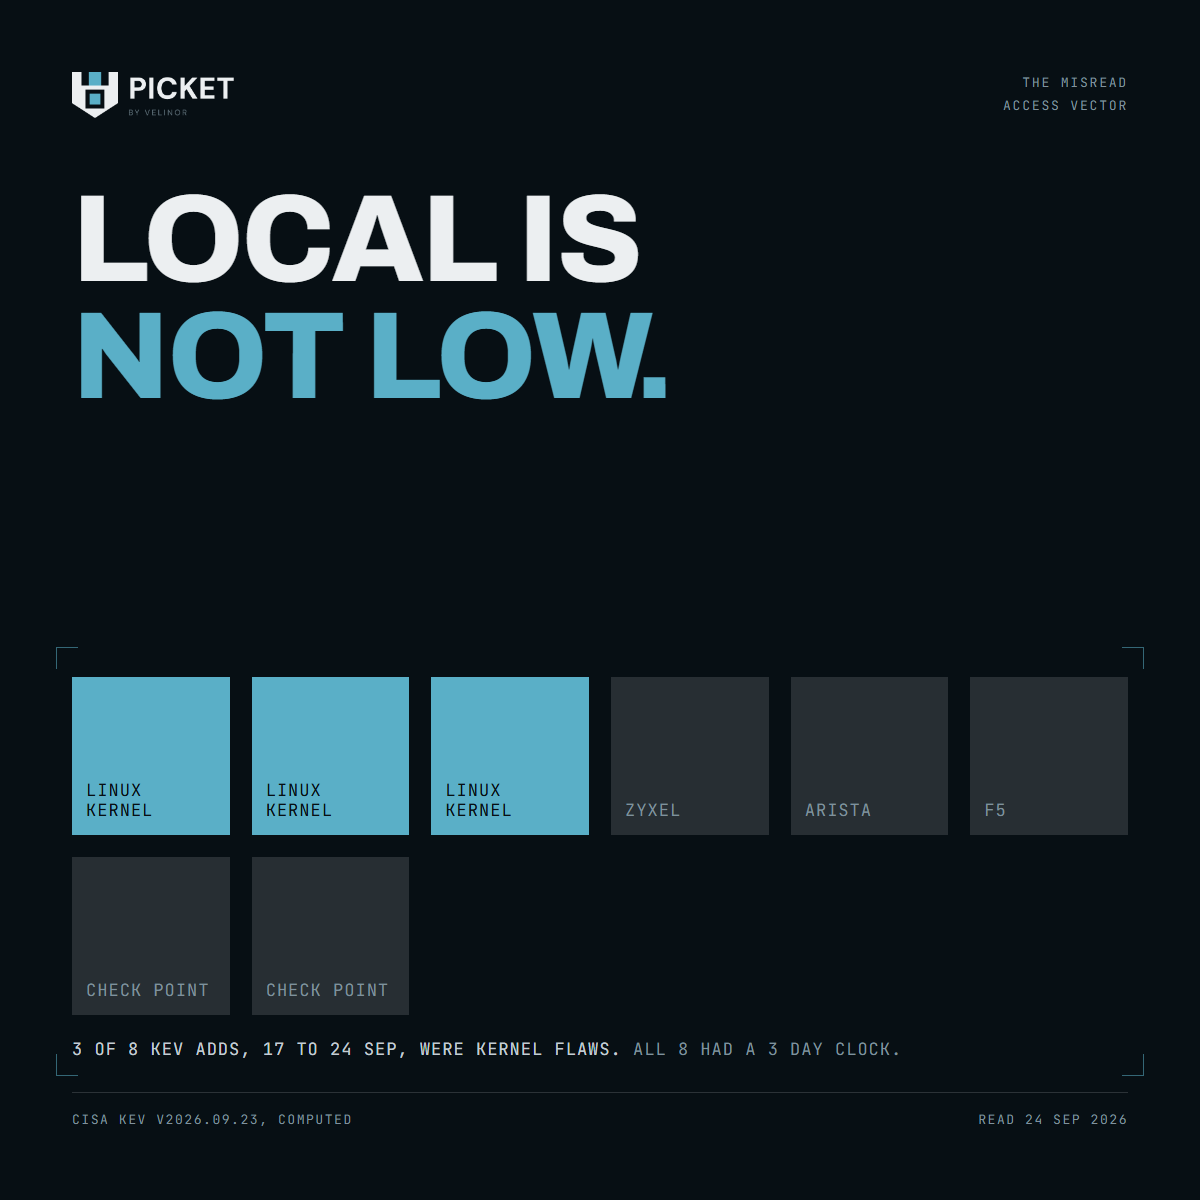
Local access required does not mean low priority. On 18 September CISA added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities catalogue in a single day.
The misread is common. Most kernel flaws need the attacker to be running code on the system already, so they score lower and wait for the next maintenance window.
That reads the flaw on its own. Intrusions are chains.
- Initial access comes from something else. An exposed appliance, a stolen credential, a vulnerable web application.
- The local flaw turns that foothold into full control of the host. Its credentials, its keys and its data.
- From there the attacker moves to the next system.
CISA gave all three kernel entries a three day deadline, the same as the five network and security products added that week.
How to treat it.
- Rank by what the finding enables and where the system sits, not by the access vector alone.
- A local flaw on a host where other people or services already run code is closer to remote than it looks. Shared servers, build agents and container hosts are the usual cases.
- If it is on the KEV list, it goes to the top of the queue with everything else on the list.
An exploited local flaw is highly likely to be used as a second step, not a first. Scoring it as if it were the first step is how it gets deferred.