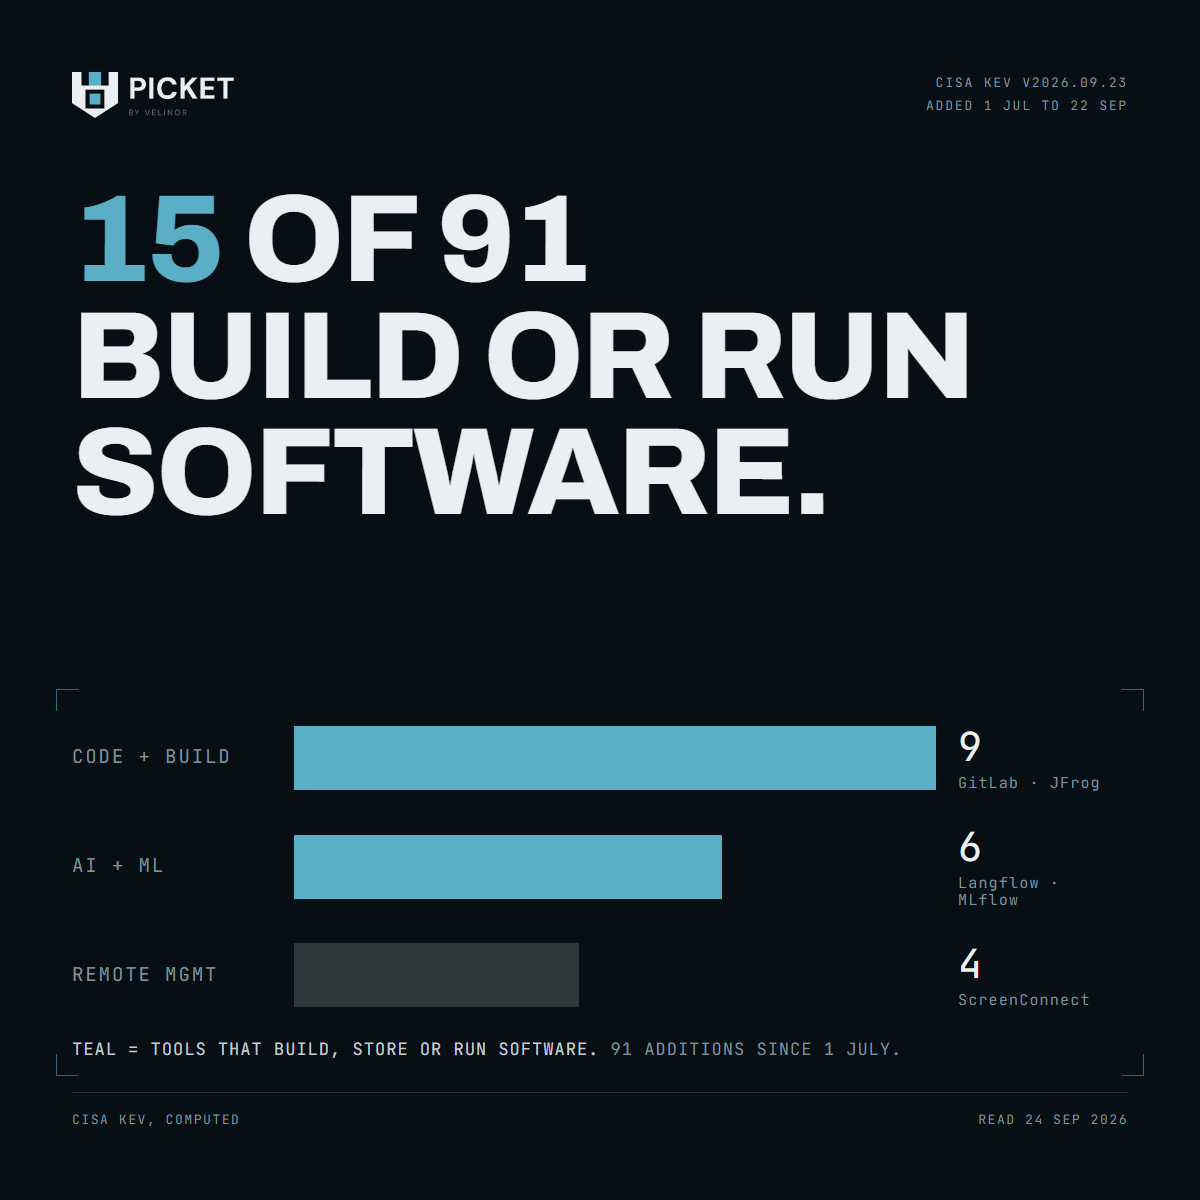
91 vulnerabilities were added to CISA's Known Exploited Vulnerabilities catalogue between 1 July and 22 September. The familiar names are there. Microsoft 11, Cisco 6, Fortinet 4, SonicWall 4.
The part worth noticing is the other column. 15 of the 91 are in tools that build, store or run software.
- Code and build. GitLab, Gitea, JetBrains TeamCity and Kestra.
- Artifact storage. JFrog Artifactory, four entries.
- AI and machine learning. Langflow, three entries, plus LiteLLM, MLflow and Ray.
- Web framework. Starlette.
Four more are remote management platforms used to run other people's estates. ConnectWise ScreenConnect, and N-able N-central with three entries.
These systems are often missing from the asset register as infrastructure. They tend to be installed by a development team, a data team or a managed service provider, sometimes in a cloud account the security team does not scan. They hold credentials, source code and the keys to production.
Two checks this week.
- Ask each engineering and data team for the self-hosted tools they run. Compare the list with what your scanner covers.
- Ask your managed service provider which remote management platform they use on your estate, which version, and who patches it.