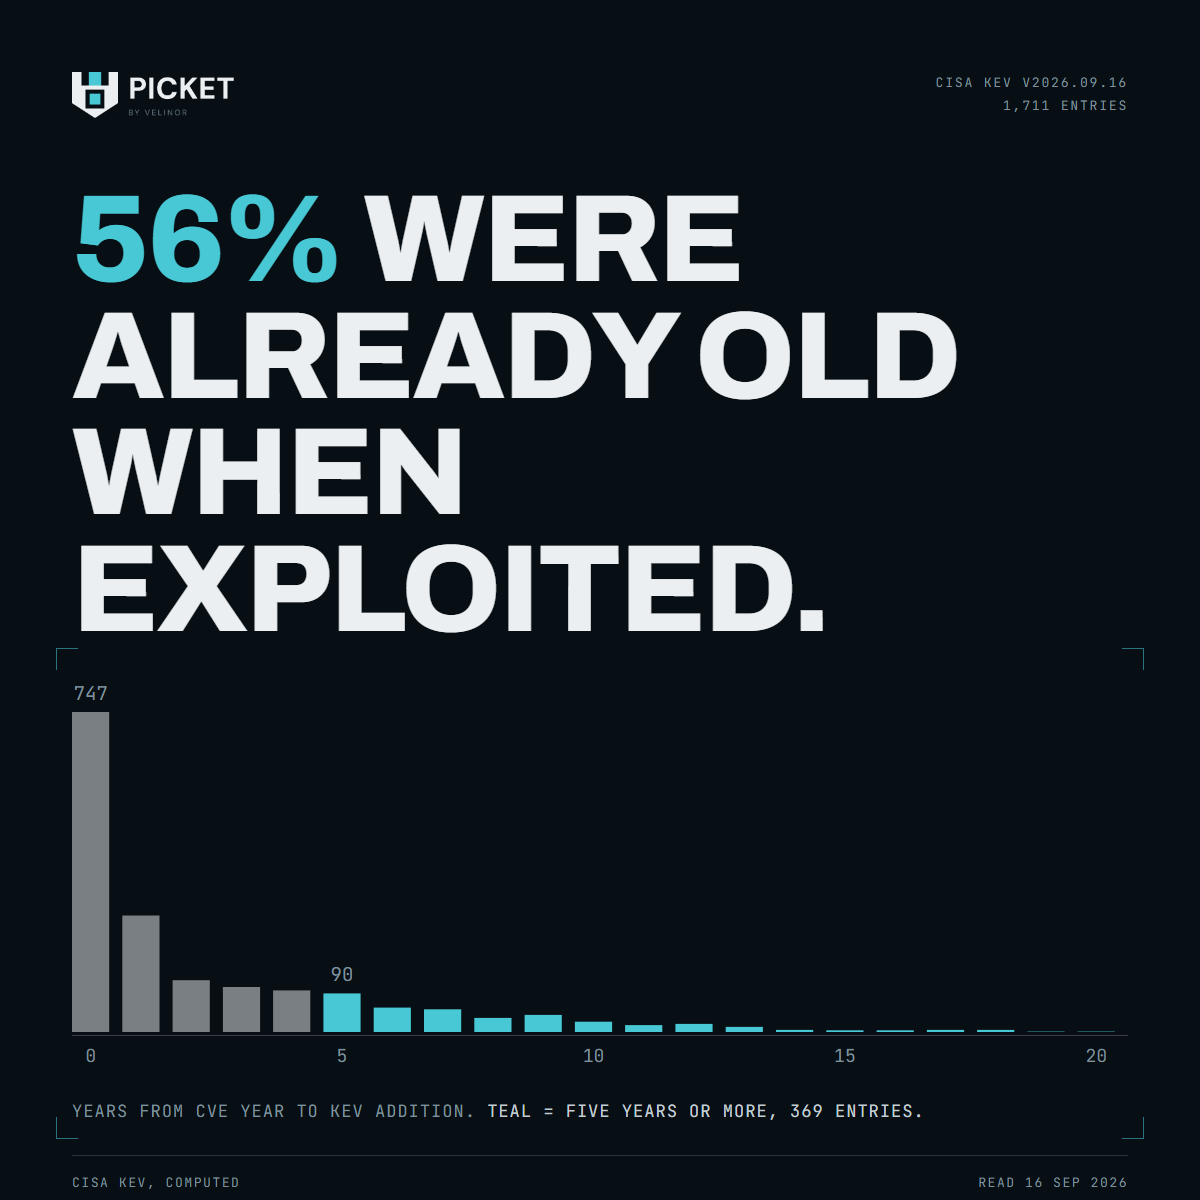
964 of the 1,711 vulnerabilities in CISA's Known Exploited Vulnerabilities catalogue were added in a later year than the year in their CVE number. That is 56%.
369 of them were five years old or more when they were added.
This year alone CISA has added 227 entries. 79 of those carry a CVE number from before 2026. Seven are from 2008 and 2009.
The lesson is not patch faster. It is that a vulnerability does not stop mattering because it is old, and a scanner that only shows you this quarter's CVEs is showing you the wrong list.
Two checks.
- Does your scanner report against the full CVE history, or a recent window?
- Does your register carry the KEV flag as its own field, so an old finding can jump the queue on the day it is added?