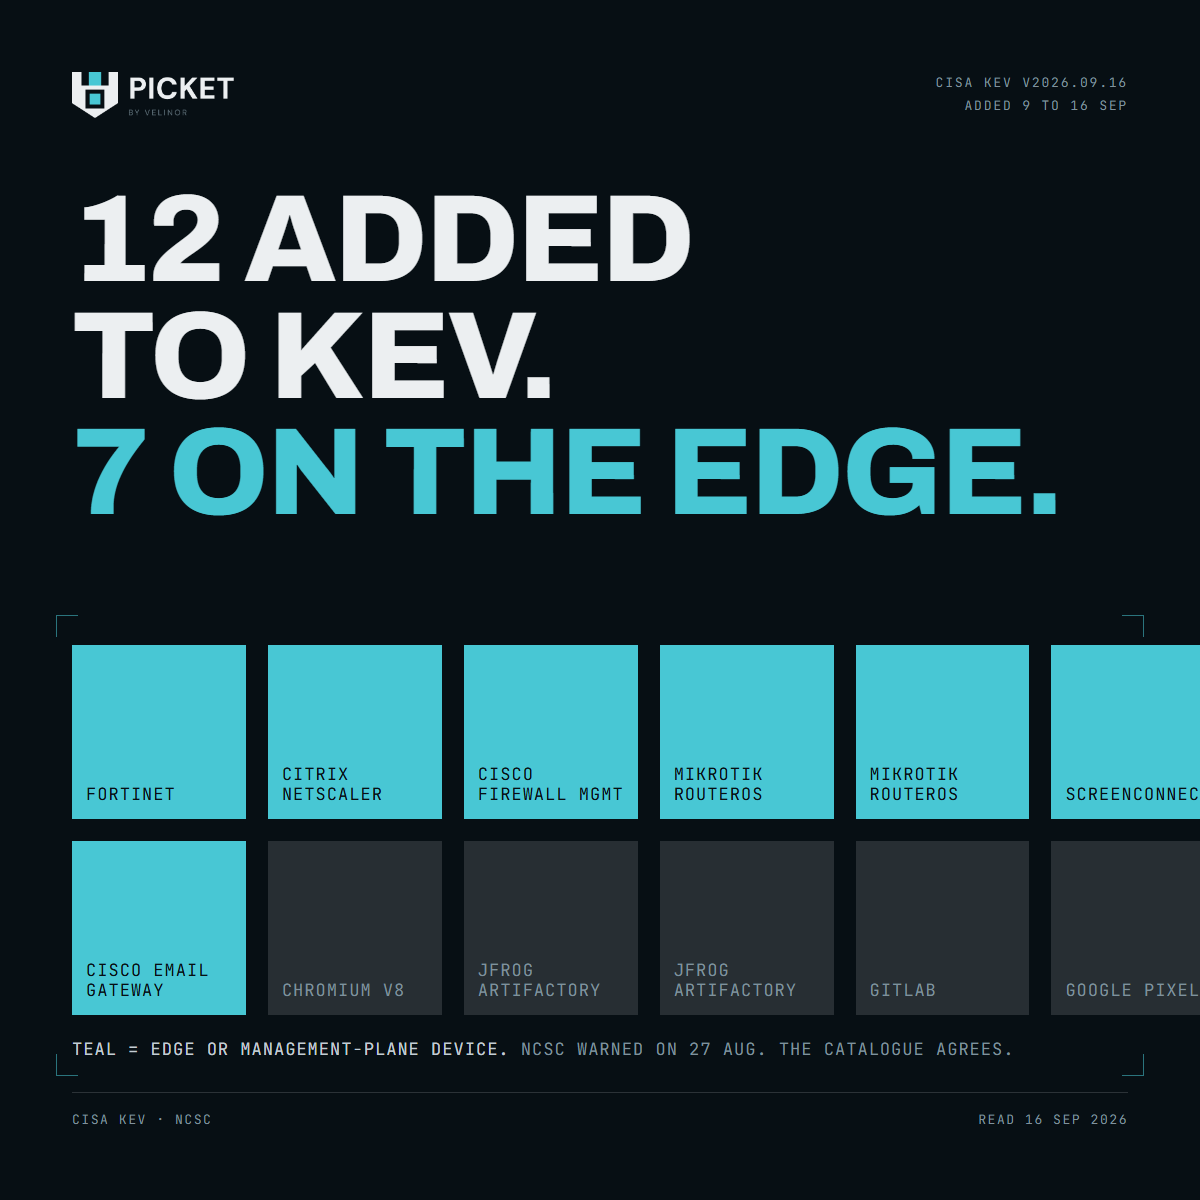
12 vulnerabilities have been added to CISA's Known Exploited Vulnerabilities catalogue since 9 September. Seven of them sit on the edge of a network or on the box that manages it.
- Cisco Secure Email Gateway
- Cisco Secure Firewall Management Center
- Citrix NetScaler
- Fortinet, multiple products (CVE-2025-25249, a 2025 CVE)
- MikroTik RouterOS, two entries
- ConnectWise ScreenConnect
The other five: JFrog Artifactory (two entries), GitLab, Chromium V8 and Google Pixel.
NCSC said the same thing on 27 August. Disruptive activity is being driven by internet-exposed systems and edge devices. The catalogue this week matches that assessment.
Three things worth doing this week if you run any of the above.
- Check the version you are actually running, not the version the change record says you are running.
- If it faces the internet and you cannot patch it this week, restrict the management interface to known addresses and write down that you did.
- Record the decision either way. A dated note that says checked and not affected is evidence. Silence is not.