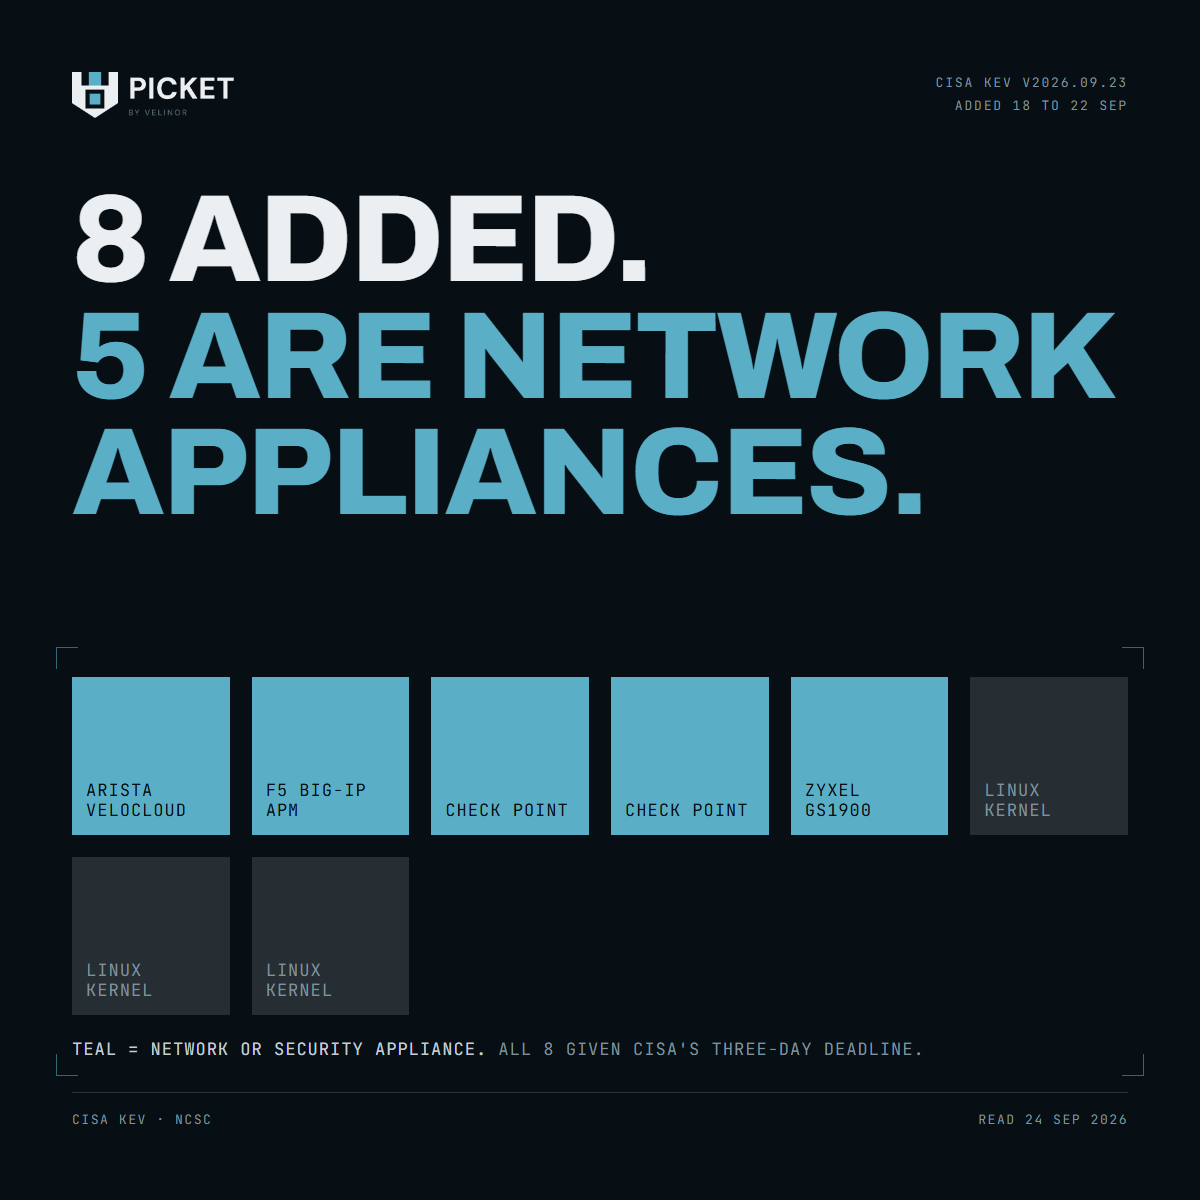
Eight vulnerabilities were added to CISA's Known Exploited Vulnerabilities catalogue between 18 and 22 September. Five of them are network or security appliances.
- Check Point, multiple products, two entries
- F5 BIG-IP APM
- Arista VeloCloud Orchestrator
- Zyxel GS1900 series switches
The other three are in the Linux kernel.
CISA gave all eight its shortest deadline, three days, for US federal agencies.
It is the second week running that network appliances lead the list. NCSC said on 27 August that disruptive activity is being driven by internet-exposed systems and edge devices. The catalogue keeps agreeing.
Three questions for this week.
- Do you have a list of every appliance that terminates remote access or manages your network? Not the ones in the design document. The ones that are switched on.
- Is the management interface of each one reachable from the internet? If it is, that is the first thing to change.
- Who is told when a vendor you run appears in the catalogue? If the answer is nobody in particular, it will be found late.