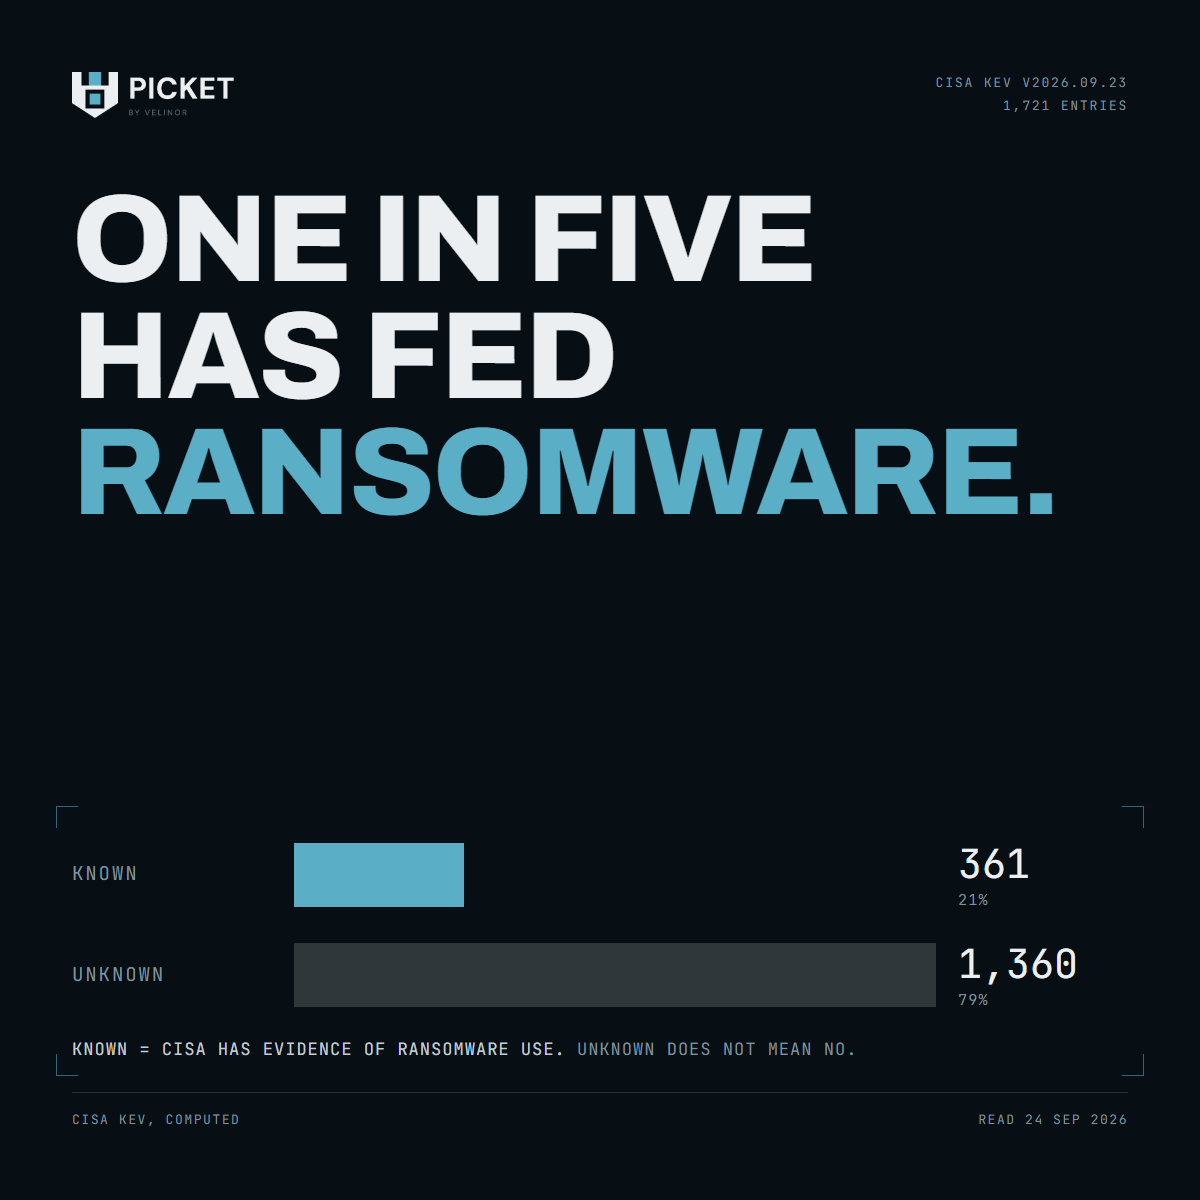
361 of the 1,721 entries in CISA's Known Exploited Vulnerabilities catalogue are marked as known to have been used in ransomware campaigns. That is 21%, roughly one in five.
The flag is worth understanding before you use it.
- Known means CISA has evidence the vulnerability was used by a ransomware operation.
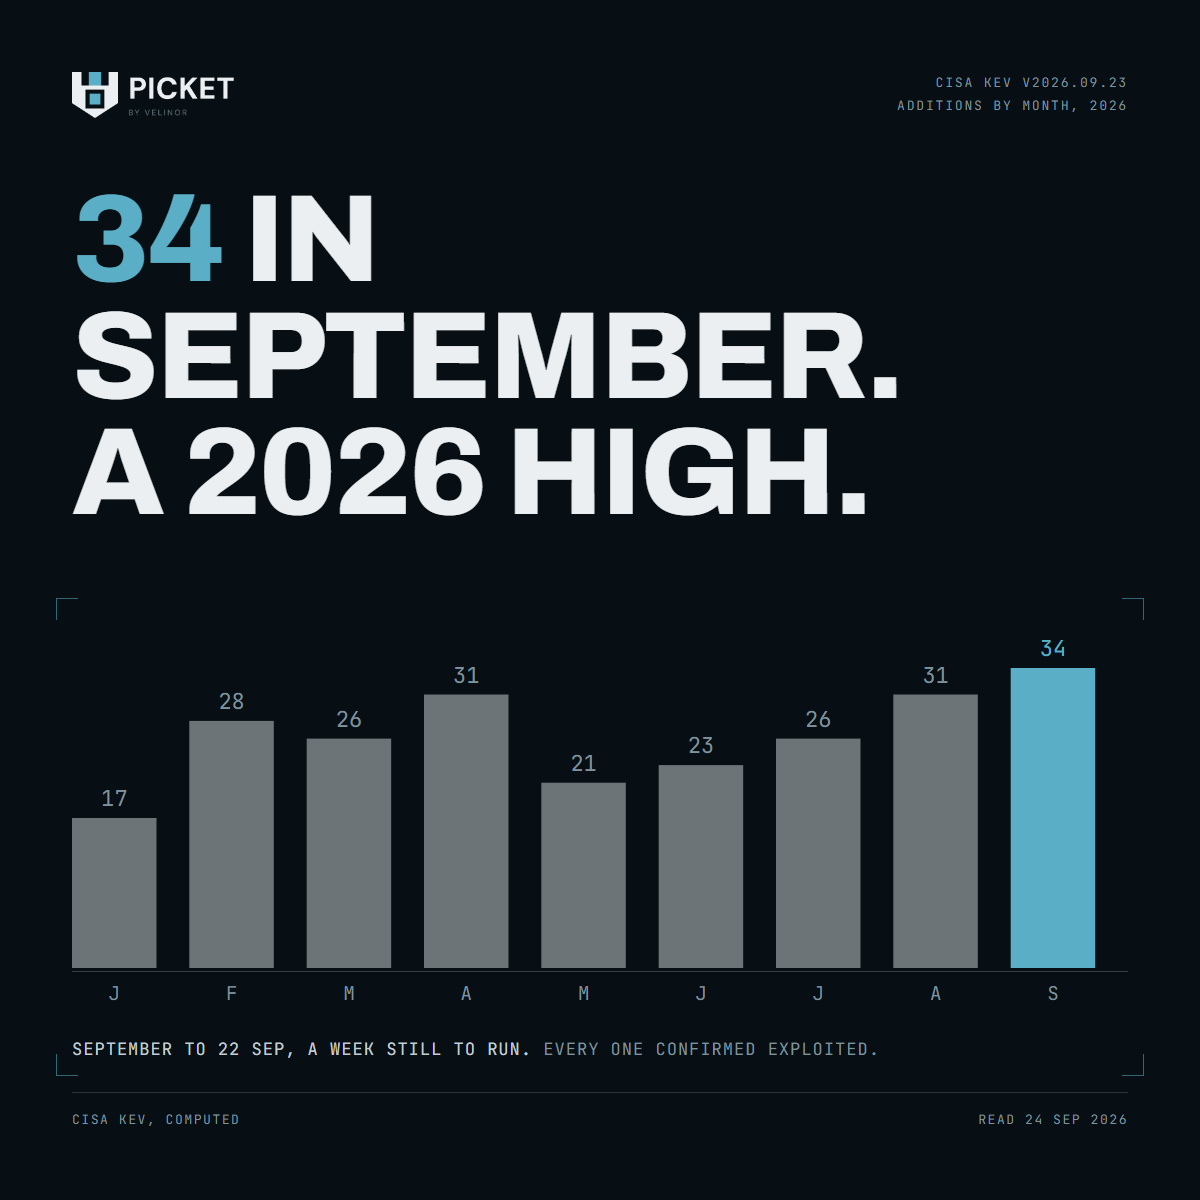
- Unknown does not mean no. It means CISA cannot confirm it either way, and the field can change after an entry is added. 27 of this year's 237 additions are marked Known so far.
- It is a field in a free, public file. You do not need a subscription to read it.
How to use it. If a finding in your estate is on the KEV list and carries the ransomware flag, it belongs at the very top of the queue. The decision to leave it open should be seen by whoever owns the business risk, not only whoever owns the server. Ransomware is a business continuity event, so leaving one open is a business decision.